In a report published on November 20, 2026, Blockstream researchers Jonas Nick and Mikhail Kudinov, with collaborators, presented a security analysis of SHRINCS, a proposed post-quantum signature scheme for Bitcoin. Kudinov asked engineers, cryptographers and protocol developers to review its draft Bitcoin Improvement Proposal. SHRINCS is a proposal, not a change to Bitcoin’s rules.
The central question is whether wallets could use it safely without making transactions too costly. SHRINCS is hash-based and draws on SHA-256, which Bitcoin already uses. It offers two ways to sign: a smaller stateful path and a larger stateless path.
The stateful path requires a wallet to track one-time signing keys. If a key’s state is accidentally reused, an attacker could forge a signature for that address and steal funds. Nick said wallet implementations must handle that state correctly and automatically fall back to the stateless path whenever its counter might be compromised.
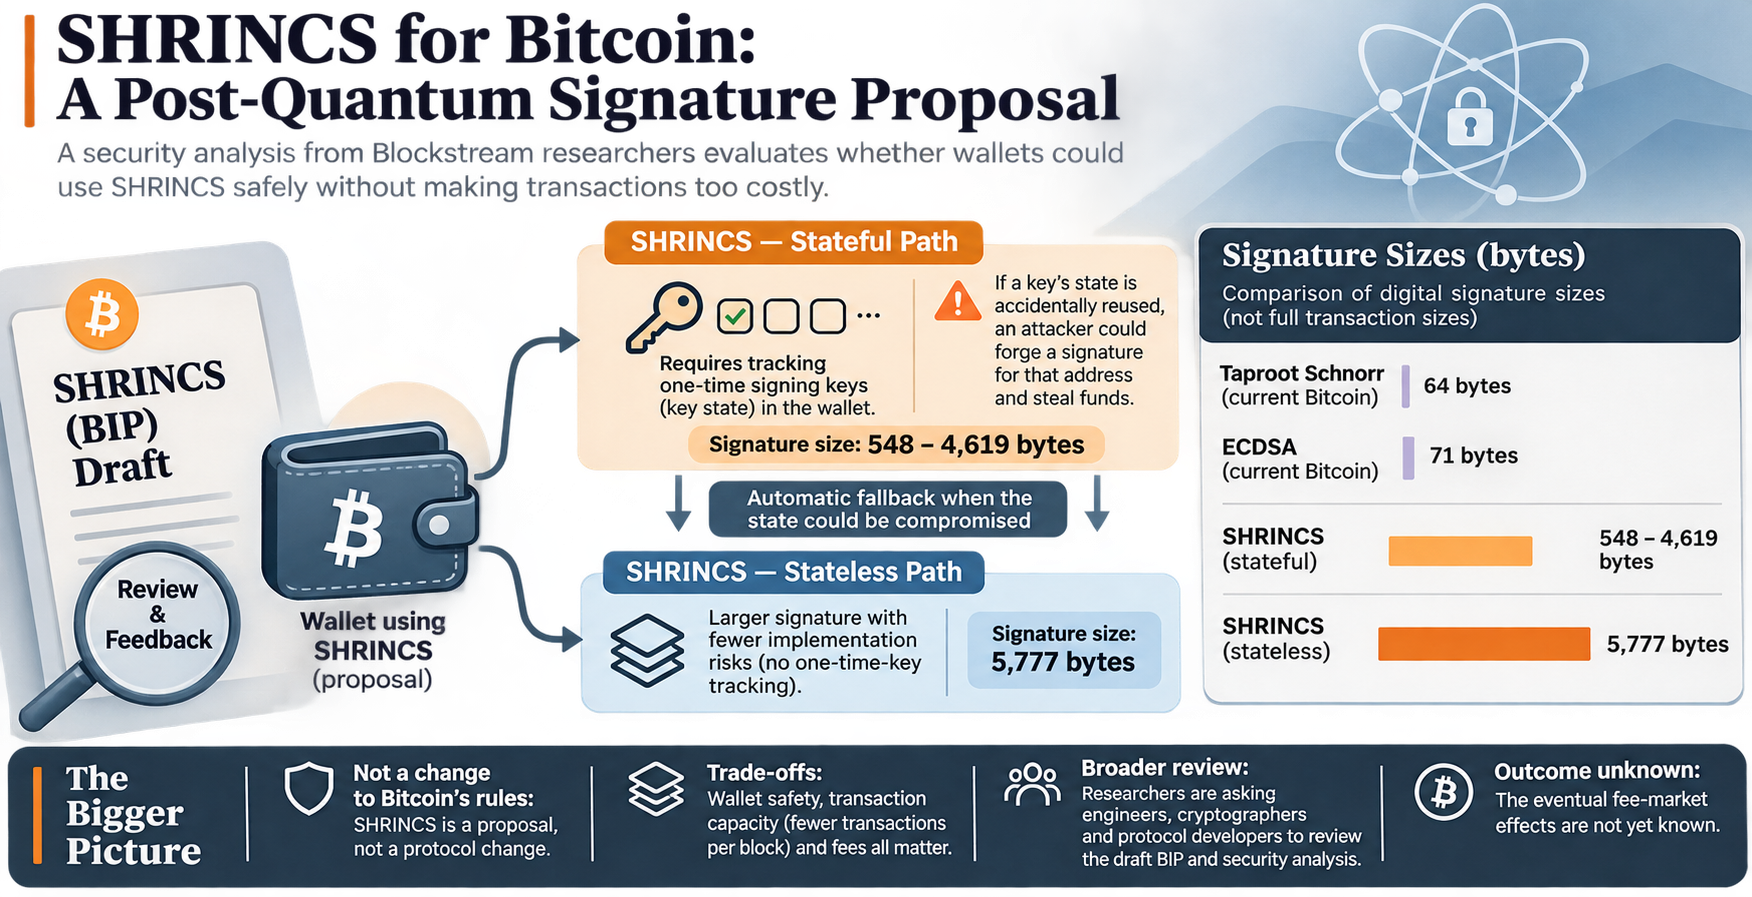
That fallback has a cost in space. The report gives signature sizes of 548–4,619 bytes for SHRINCS’ stateful path and 5,777 bytes for its stateless path, compared with typically 71 bytes for Bitcoin’s current ECDSA signatures and 64 bytes for Taproot Schnorr signatures. Nick warned that widespread use of larger signatures could leave room for fewer transactions per block and affect fees, while saying the eventual fee-market effects are unknown.
The remaining trade-off is therefore not just cryptographic strength. Wallet safety, transaction capacity and broader review all matter before the proposal’s suitability for Bitcoin can be judged.